
MyTechDailyNews General: ConnectWise Supply Chain Attack, Storm-0940 and Microsoft 365 Explained
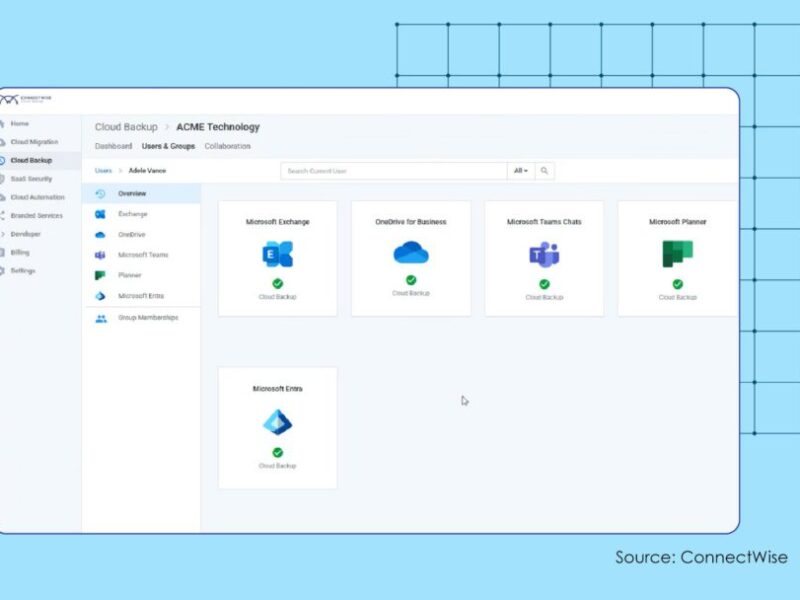
In this MyTechDailyNews General explainer, the ConnectWise incident reads as a trust problem more than a mystery AI attack. Microsoft says a China-aligned intrusion group, Storm-0940, used AI agents to push a supply-chain compromise into Microsoft 365 at speed, with credentials tied to ConnectWise cloud applications. The attempted access reportedly reached more than 2,250 Microsoft 365 tenants by leaning on permissions already granted to those applications.
What happened and who is behind it
Microsoft published its threat intelligence report on 21 October, stating that Storm-0940 had relied on the ARTEX agentic penetration-testing framework since at least September 2026. The reported target set included aerospace, automotive, energy, government, manufacturing and semiconductor organisations. ARTEX is described as a multi-agent system that applies large language models to offensive security work, from reconnaissance and vulnerability discovery to exploitation. A Go backend supports it, a Next.js interface provides interaction, and it can work with different AI models.
Although ARTEX was designed for penetration testing, the framework can be used to automate malicious activity with relatively little human intervention. In this case, that automation appears to have shortened the gap between a stolen or abused application connection and attempted access across a large estate of Microsoft 365 tenants.
Two attack paths: password spray and trusted application sign-in
Between 10 and 14 October, Microsoft observed a separate password-spraying campaign associated with Storm-0940 that targeted 327 accounts at eight organisations. More than 151,000 authentication attempts failed, with a peak of 2,900 failures per minute, and Microsoft found no successful authentication in that campaign.
The ConnectWise route was different. Rather than guessing user passwords, attackers authenticated as trusted third-party applications, bypassing the need for an interactive user sign-in. Microsoft observed follow-on Microsoft Graph operations in some tenants, including reconnaissance, credential changes and attempts to alter privileges. Across the wider campaign, Storm-0940 obtained privileged cloud access within three hours of initial targeting in several ARTEX-assisted attacks.
Microsoft cautioned that a successful application sign-in does not, by itself, establish that customer data was accessed or stolen. Even after the original compromised connection has been disabled, however, credentials added to other applications can preserve unauthorised access.
Service disruption: ConnectWise Cloud Backup, SaaS Security and Cloud Management
On 14 October, ConnectWise said it discovered unauthorised access involving application identities for Cloud Backup, previously known as SkyKick. The company suspended Cloud Backup and, because the services share integrations, also suspended SaaS Security and Cloud Management. According to the company's 23 October security update, restoration testing was expected to continue through the weekend, with access to existing backups potentially returning in phases the following week.
The company says existing backup archives remain encrypted and isolated, with no indication of compromise. Nevertheless, individual Microsoft 365 tenants require investigation for persistent credentials, unexpected privilege assignments and unauthorised activity. Microsoft's guidance is to keep the affected application connections disabled until ConnectWise authorises their restoration, while preserving sign-in and audit records.
Why this matters for ordinary users and tech teams
The attack provides a specific example of AI speeding up established cybercrime techniques rather than introducing an entirely new route into organisations. For non-specialist readers, the practical lesson is that a breach can spread through trust already granted to software tools, not only through weak passwords or obvious email traps. Earlier eeNews Europe reporting on AI-enabled data breaches also examined the growing role of AI in attacks.
Action checklist for Microsoft 365 teams
- Review application authentication records for sign-ins tied to affected ConnectWise cloud application identities, especially any activity after 14 October.
- Search for unexpected Microsoft Graph usage, credential changes, privilege modifications or data-access reconnaissance.
- Disable affected ConnectWise application connections and keep them disabled until ConnectWise authorises restoration.
- Look for persistent credentials or OAuth grants added to other applications, since these can preserve access after the original connection is cut.
- Preserve sign-in and audit logs before remediation changes alter evidence.
- Treat recovery as staged: backup access may return in phases, with testing expected through the weekend and partial access possibly in the following week, per the 23 October update.
Common misconceptions
- “Application sign-in means customer data was stolen.” Not necessarily; Microsoft says a successful application sign-in does not, by itself, establish that customer data was accessed or stolen.
- “Disabling one connection ends the problem.” Even after the original compromised connection has been disabled, credentials added to other applications can preserve unauthorised access.
- “This is an entirely new AI cyberattack.” The report frames it as AI speeding up established techniques.
FAQ
Who is Storm-0940?
Microsoft says Storm-0940 is a China-aligned hacking group linked to the ConnectWise supply chain attack and to attempts involving more than 2,250 Microsoft 365 tenants.
What are ARTEX AI agents?
ARTEX is an agentic penetration-testing framework. It uses a multi-agent system, a Go backend, a Next.js interface and large language models to automate tasks such as reconnaissance, vulnerability discovery and exploitation.
Which services were affected?
ConnectWise reported unauthorised access involving Cloud Backup, previously known as SkyKick, and suspended Cloud Backup, SaaS Security and Cloud Management because they share integrations.
When were the main updates published?
Microsoft's report was published on 21 October. ConnectWise disclosed the initial unauthorized access on 14 October and issued a security update on 23 October.
What should teams do next?
They should investigate persistent application credentials, review Microsoft Graph activity, preserve audit records and keep affected application connections disabled until vendor restoration is authorised.